The agentic desktop connector
Signed software from the bank that connects a customer's AI app to the bank's APIs. The customer no longer hands the AI a password or lets it read the screen.
Customers already use AI to do their banking
They do it in one of two ways. Neither is safe.
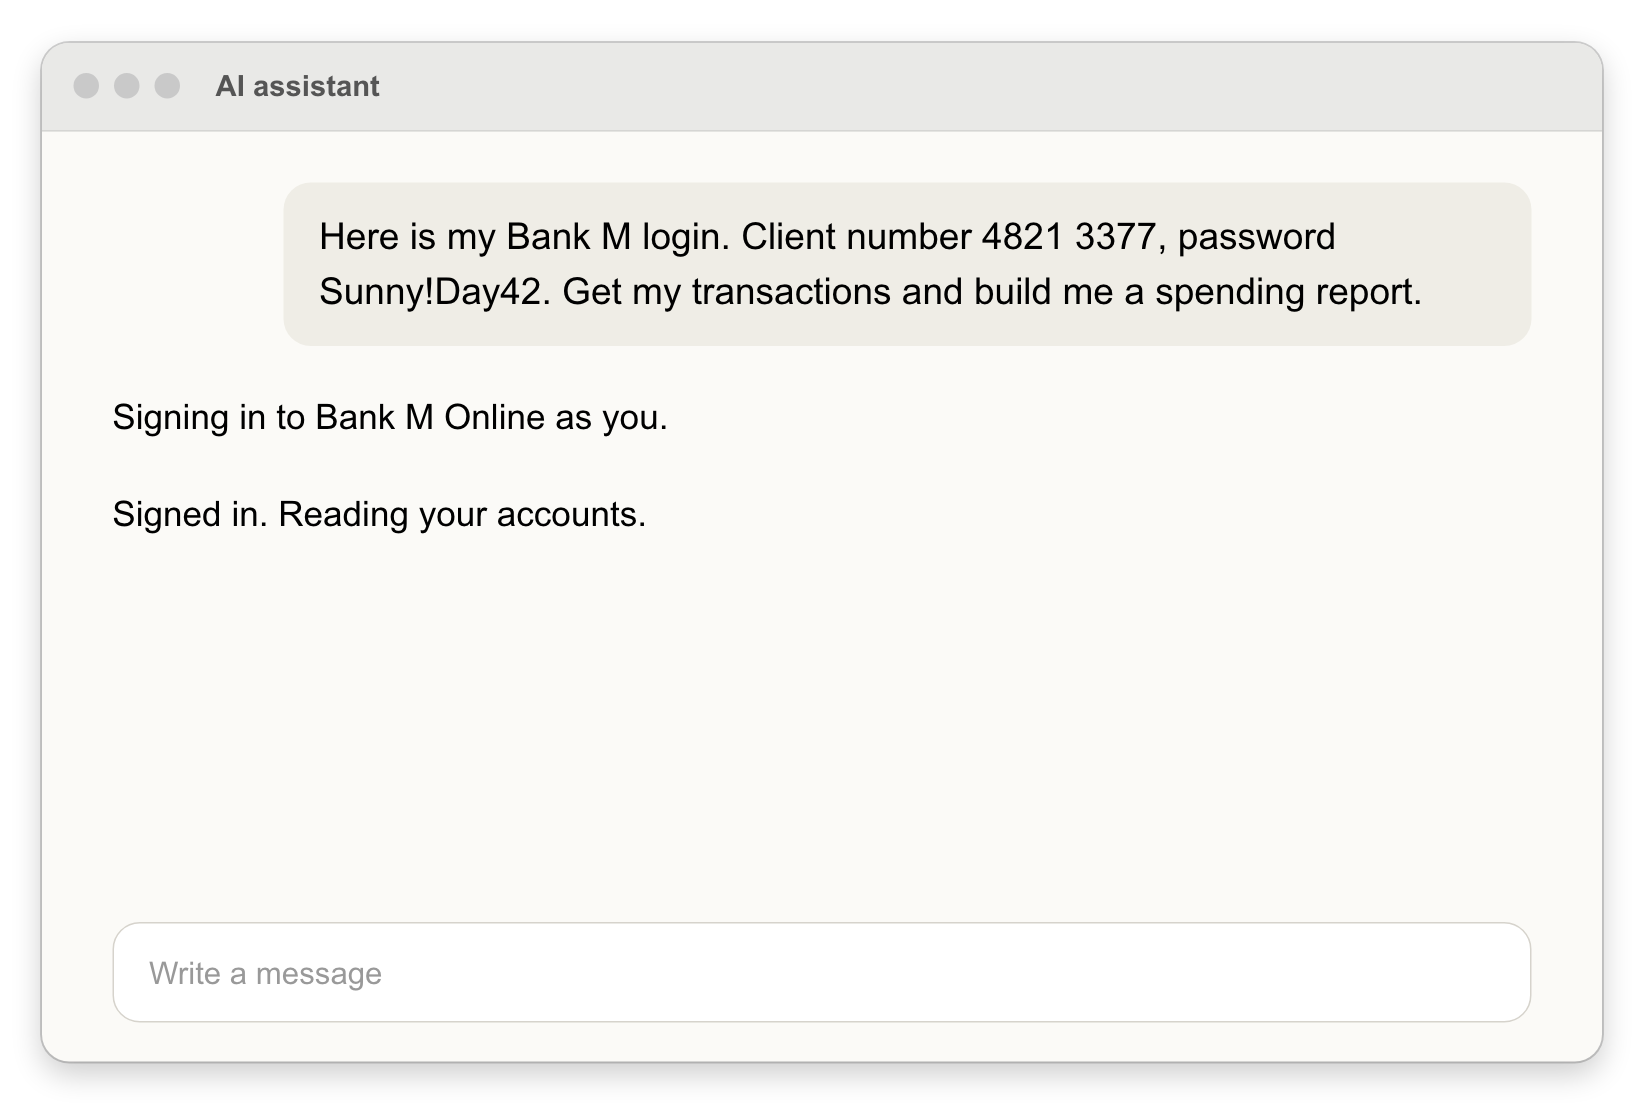
Give the AI the password
The AI signs in as the customer. The password is now outside the customer's control.
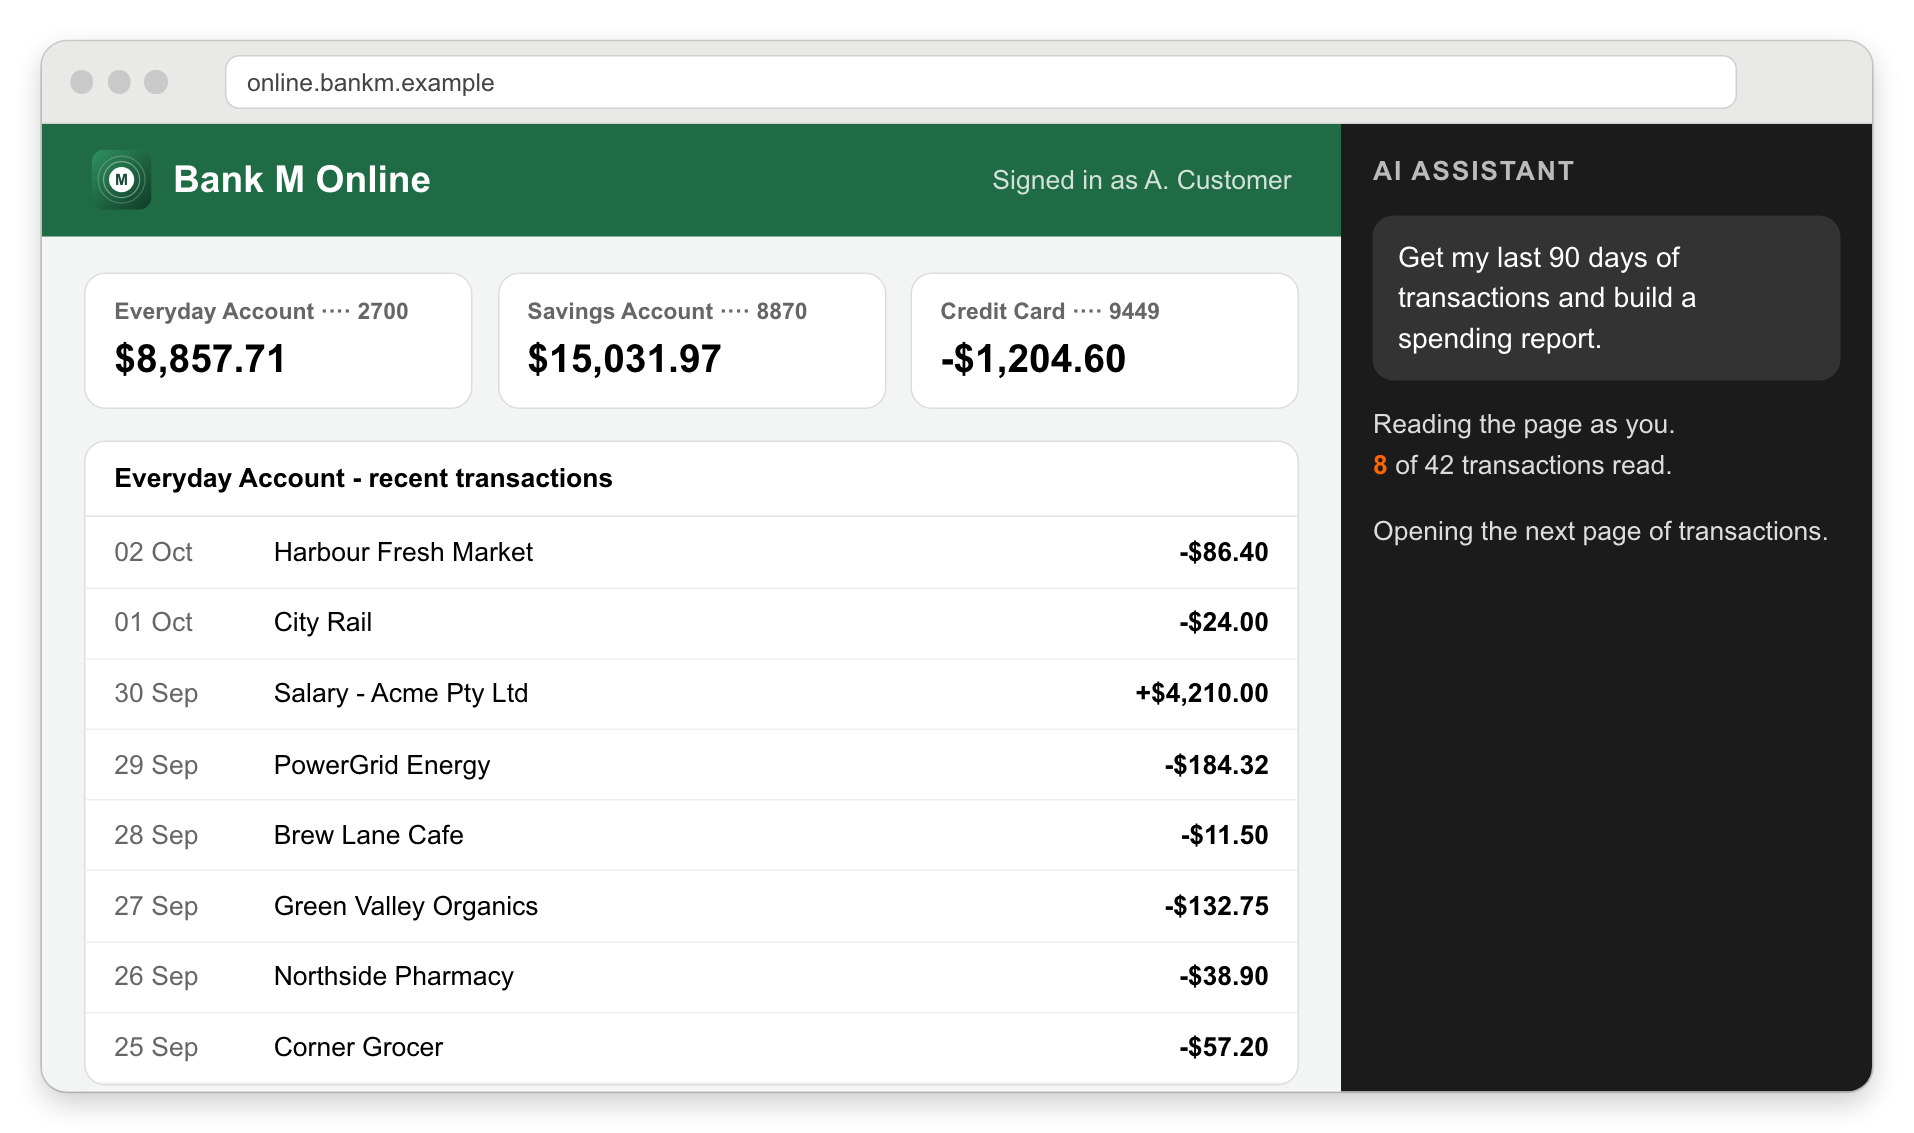
Sign in and let the AI read the screen
The AI works inside the customer's session. The bank sees one session and cannot tell the AI from the customer.
The AI gets full access
It sees every account and can do anything the customer can do, including payments.
The customer cannot limit it
There is no way to share one account only, or to allow reading and block paying.
The bank cannot see it or stop it
It sees a normal customer session, with no record of consent and nothing to revoke.
A secure way to do the same job
The connector runs on the customer's desktop. The AI app starts it and calls its tools. The connector calls the bank's APIs with an access token bound to its own key. The customer approves in the bank's app on their phone.
The AI never holds the customer's password. The bank's control plane lists every connector instance and can revoke any one of them.
| Password or screen reading | Agentic desktop connector | |
|---|---|---|
| What the AI holds | The customer's password, or their signed-in session | A grant for the accounts the customer chose |
| What the AI can do | Everything the customer can do | Only what the customer approved |
| Payments | The AI can pay as the customer | Each payment needs the customer's approval in the bank's app |
| What the bank sees | A normal customer session | One named connector instance on one desktop |
| How access is removed | The customer changes the password | The bank or the customer revokes that one instance |
Five steps, with the customer present
Install, scan, confirm, choose accounts, then ask. Nothing is shared until the customer approves on the phone and on the desktop.
The customer installs signed software from the bank
- The bank publishes the connector. The customer installs it like any other desktop app.
- The operating system checks the signature before the connector runs.
- The connector runs in the background. The customer adds it to their AI app.
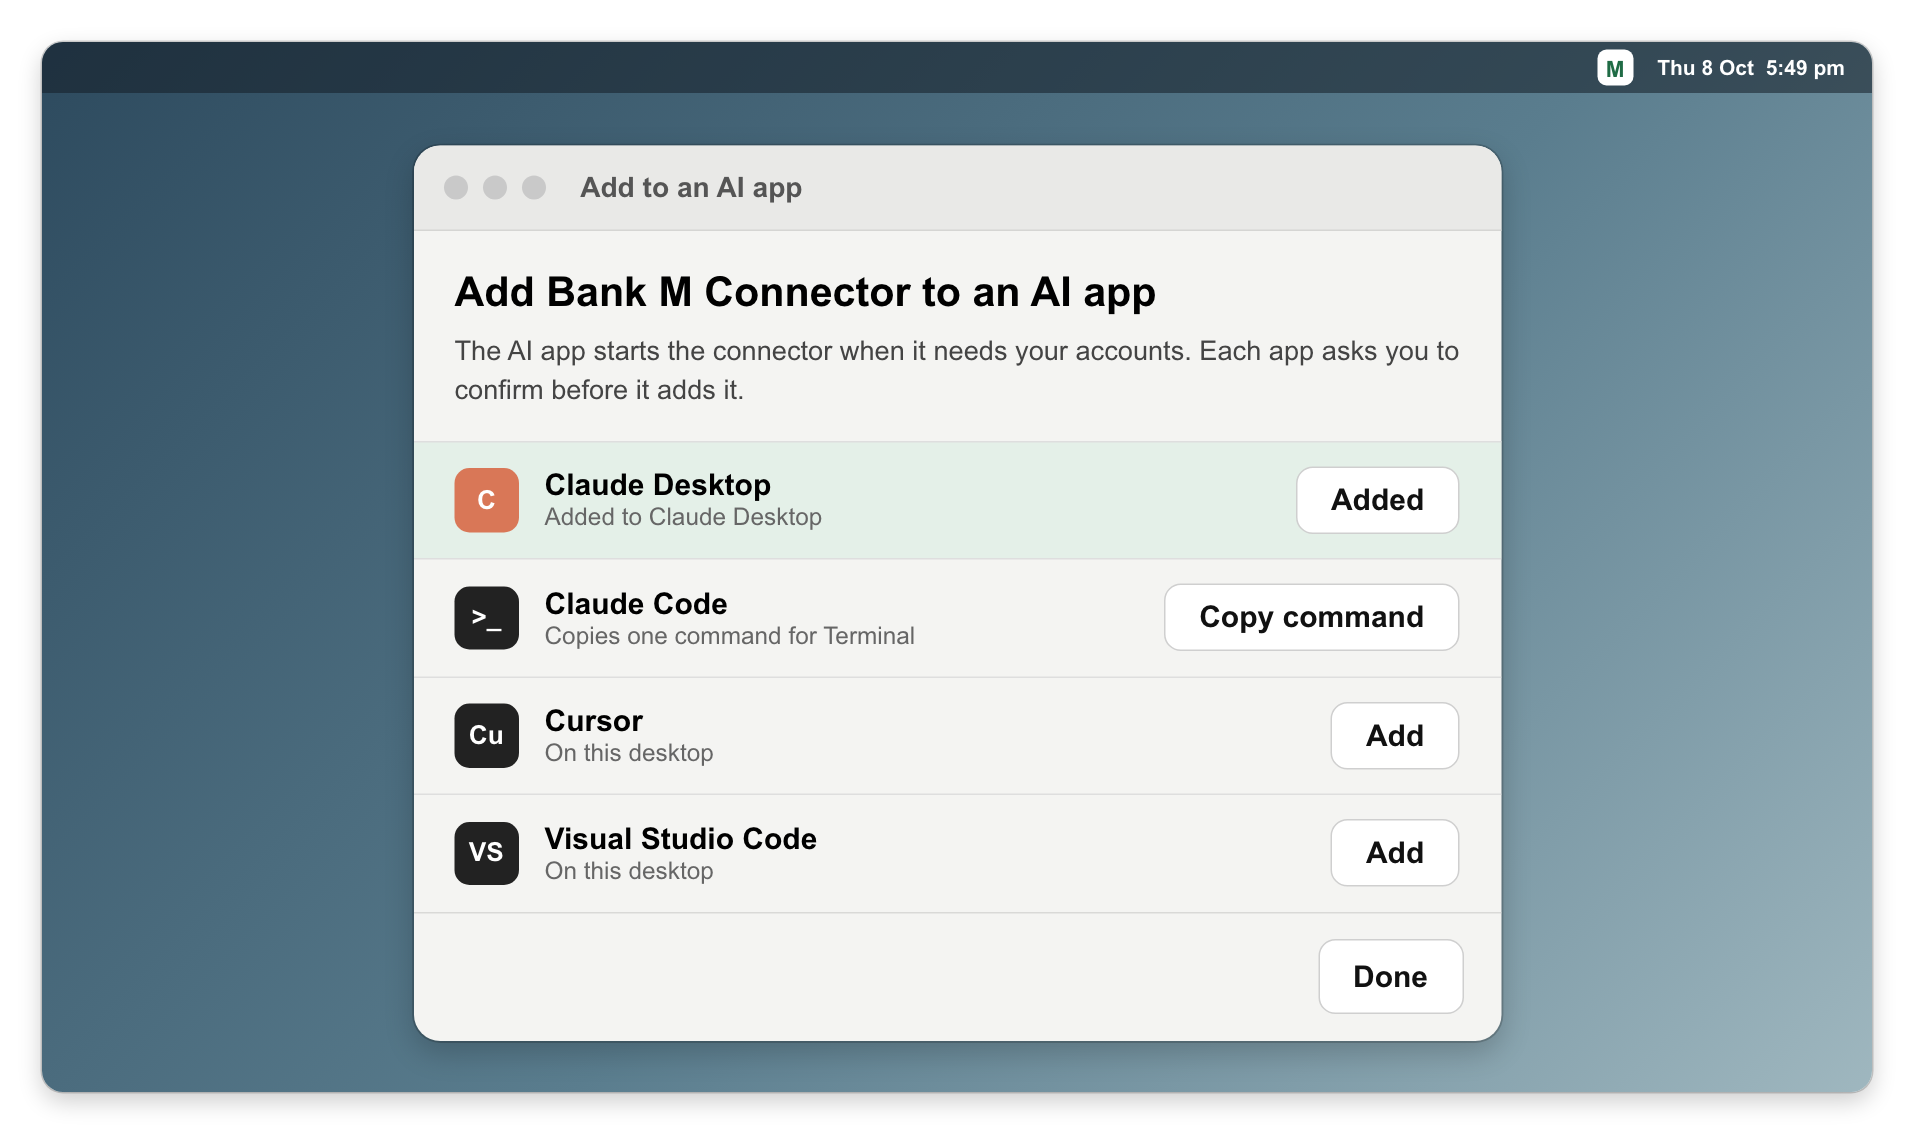
The customer scans a code and must be present
- The AI app asks to connect. The connector shows a QR code.
- The customer opens the bank's app with Face ID and scans the code.
- The phone and the desktop check each other over Bluetooth.
- A scammer in another place cannot complete the binding.
Both devices show the same code
- The desktop and the phone show the same six-digit code.
- No code, or a different code, means someone else may be trying to connect.
- The customer confirms on the desktop and keeps the connection.
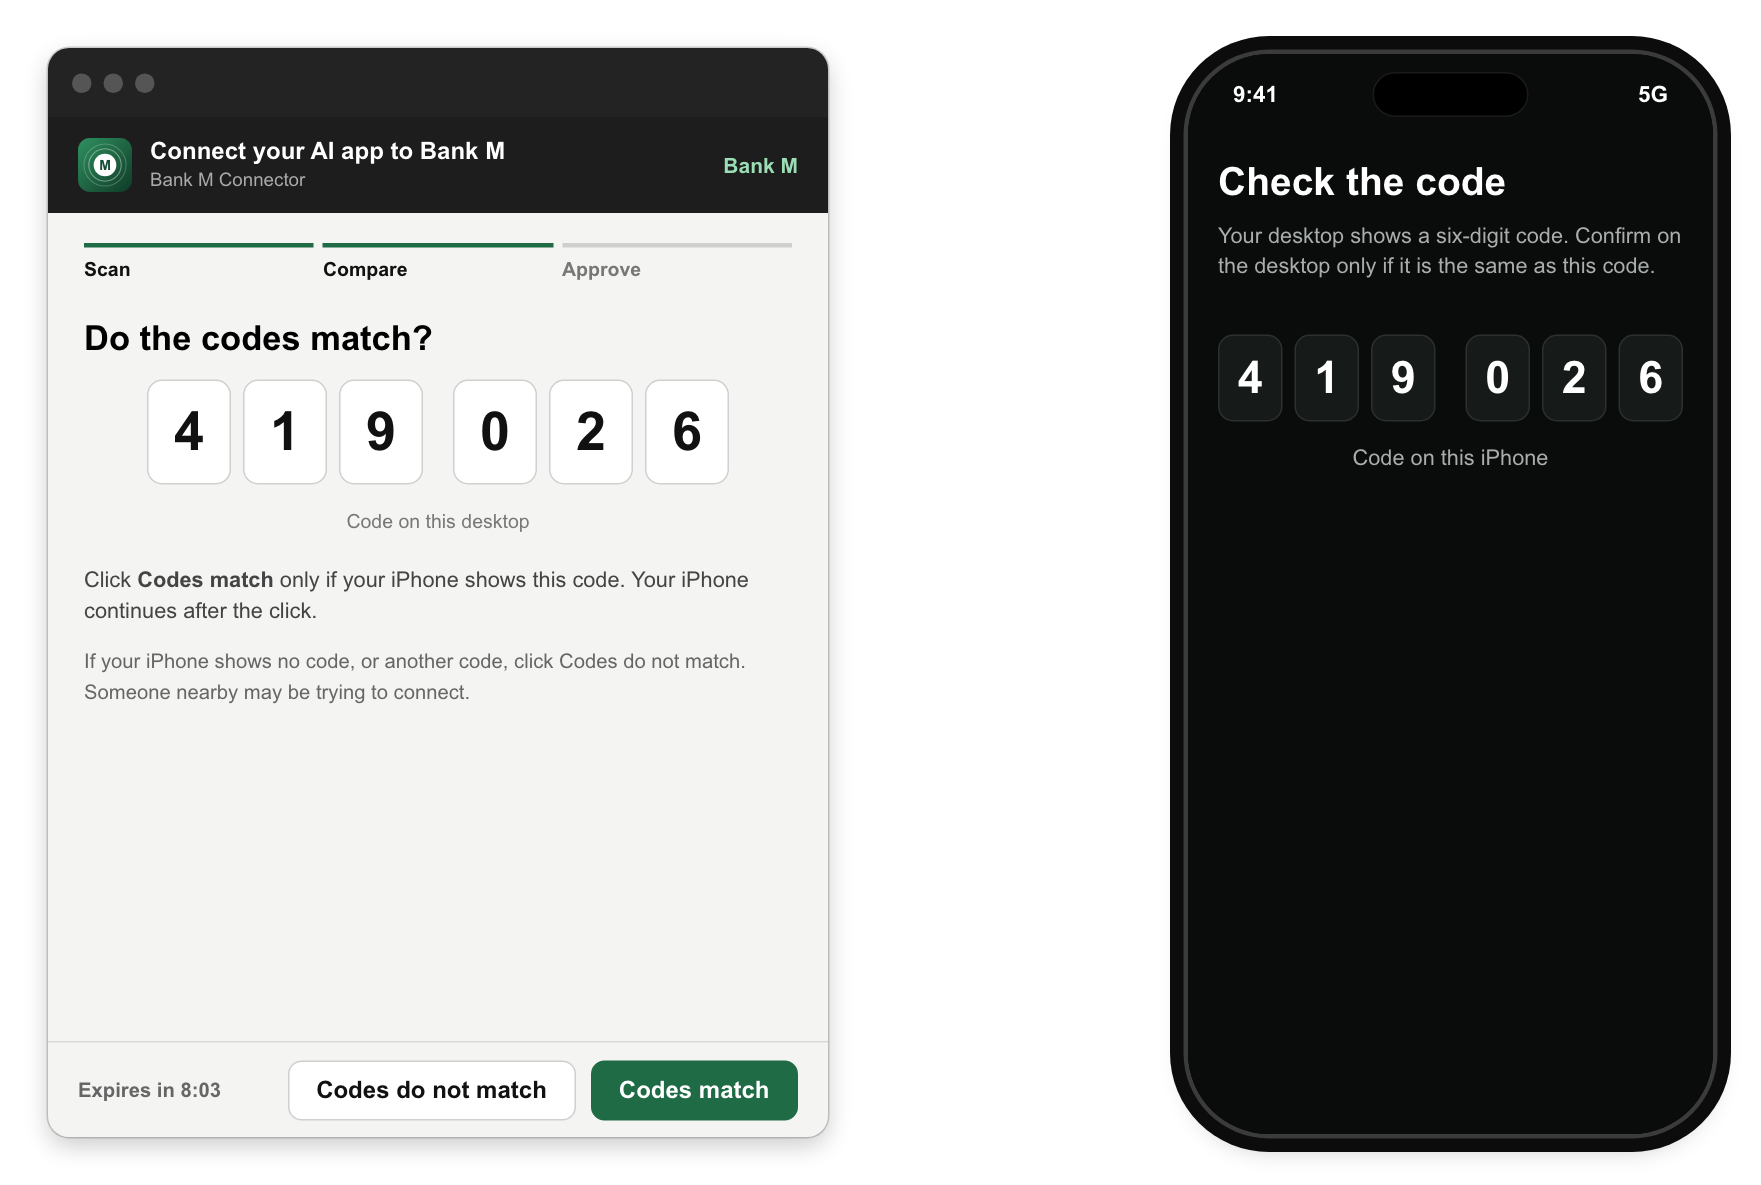
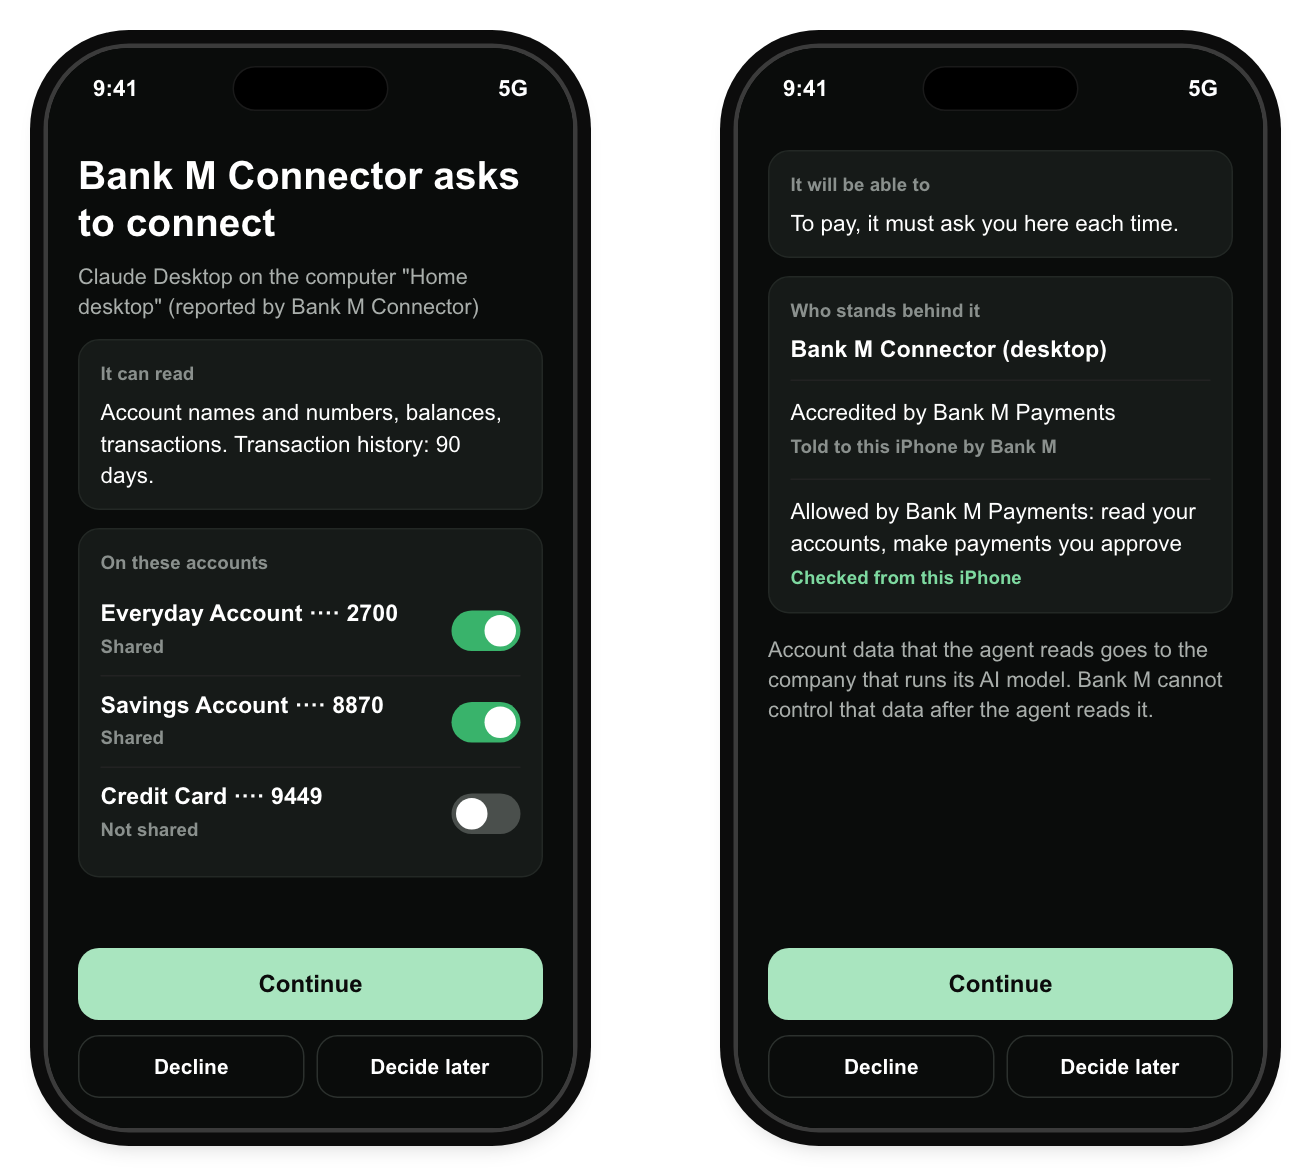
The customer chooses which accounts to share
- Every account starts as Not shared. The customer turns on the ones to share.
- The app shows who accredits the connector and what it is allowed to do.
- Payments are separate. To pay, the connector must ask in the app each time.
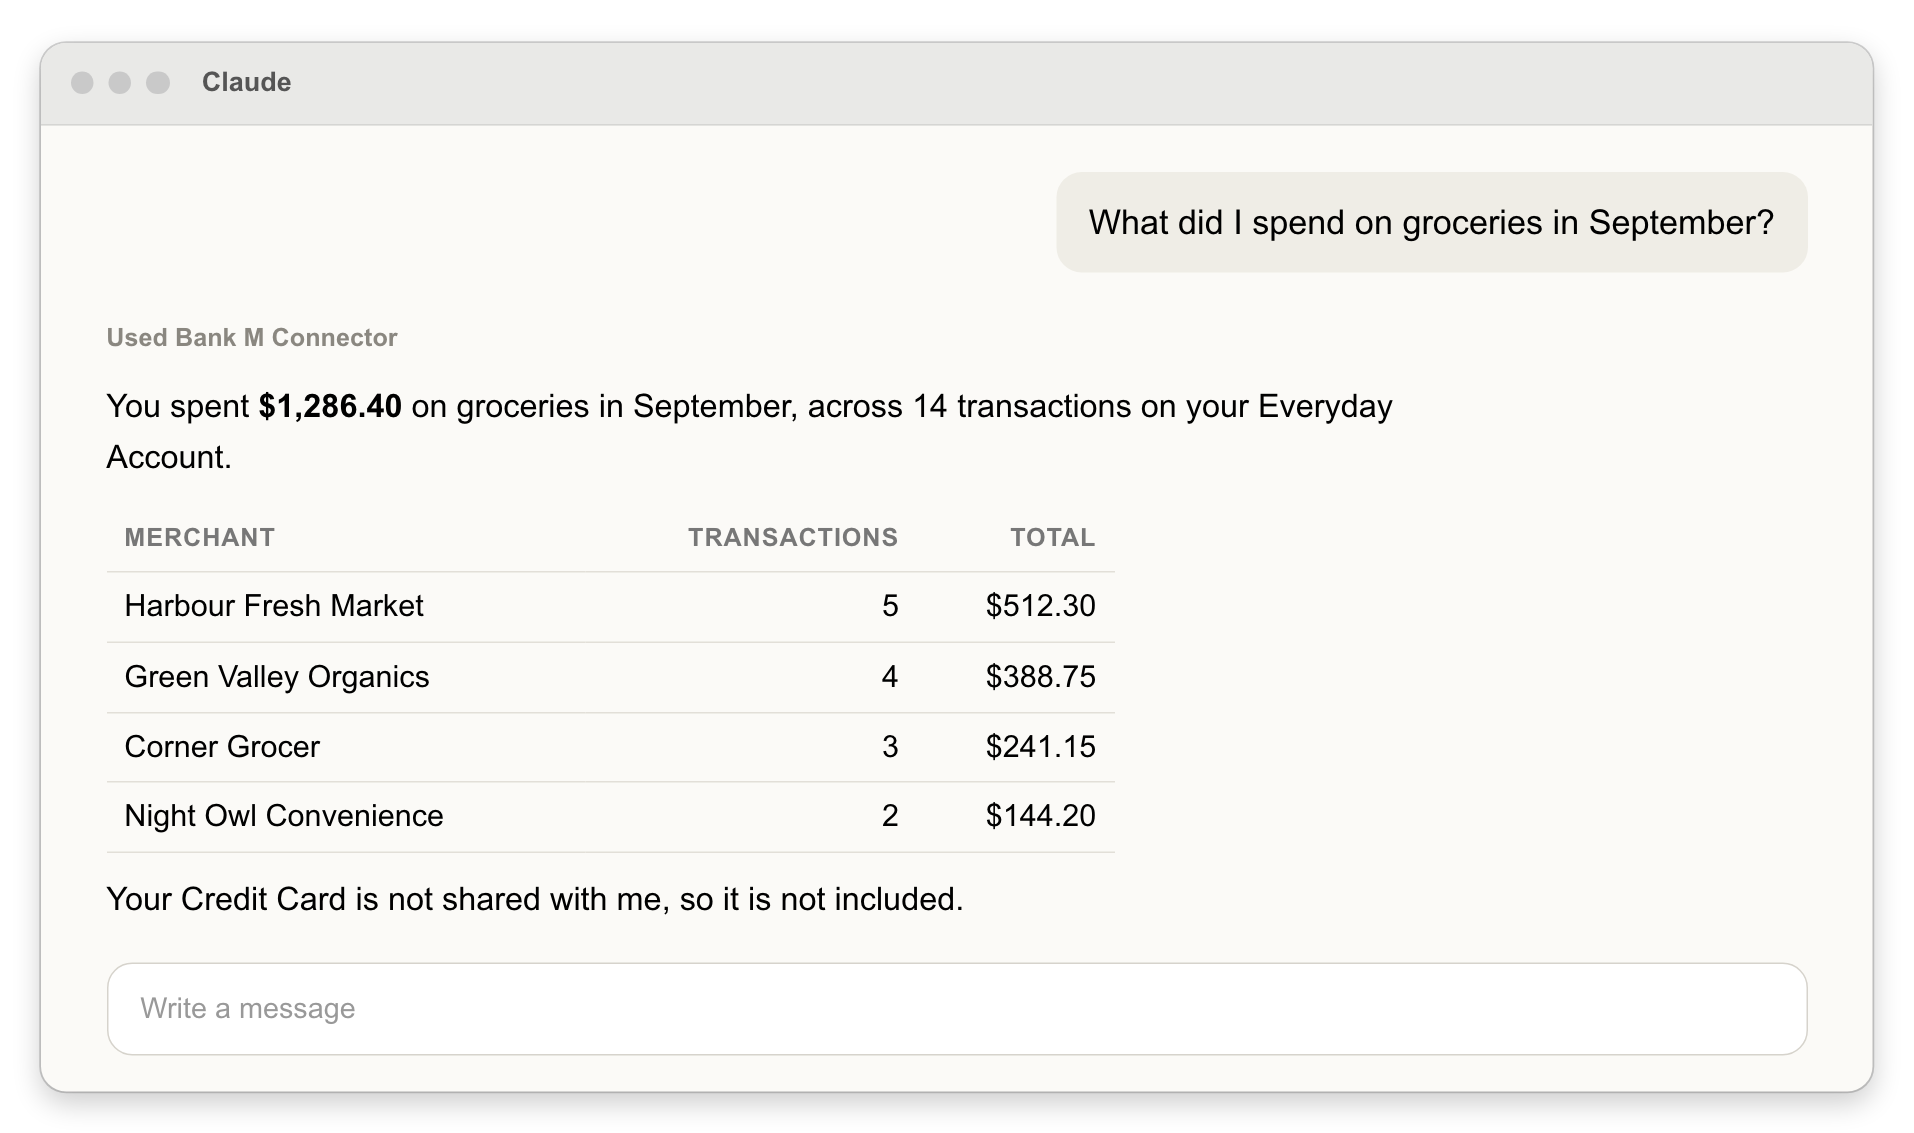
The AI reads only the shared accounts
- The customer asks their AI app about their banking.
- The AI app asks before it uses a tool from the connector.
- It reads through the bank's own API. No password. No screen reading.
One attested copy, one desktop, one customer
Every instance is a node the bank can see and revoke
Customer desktops sit in the public zone. Staff desktops inside the bank can run connectors too. Each instance has its own key and its own grant.
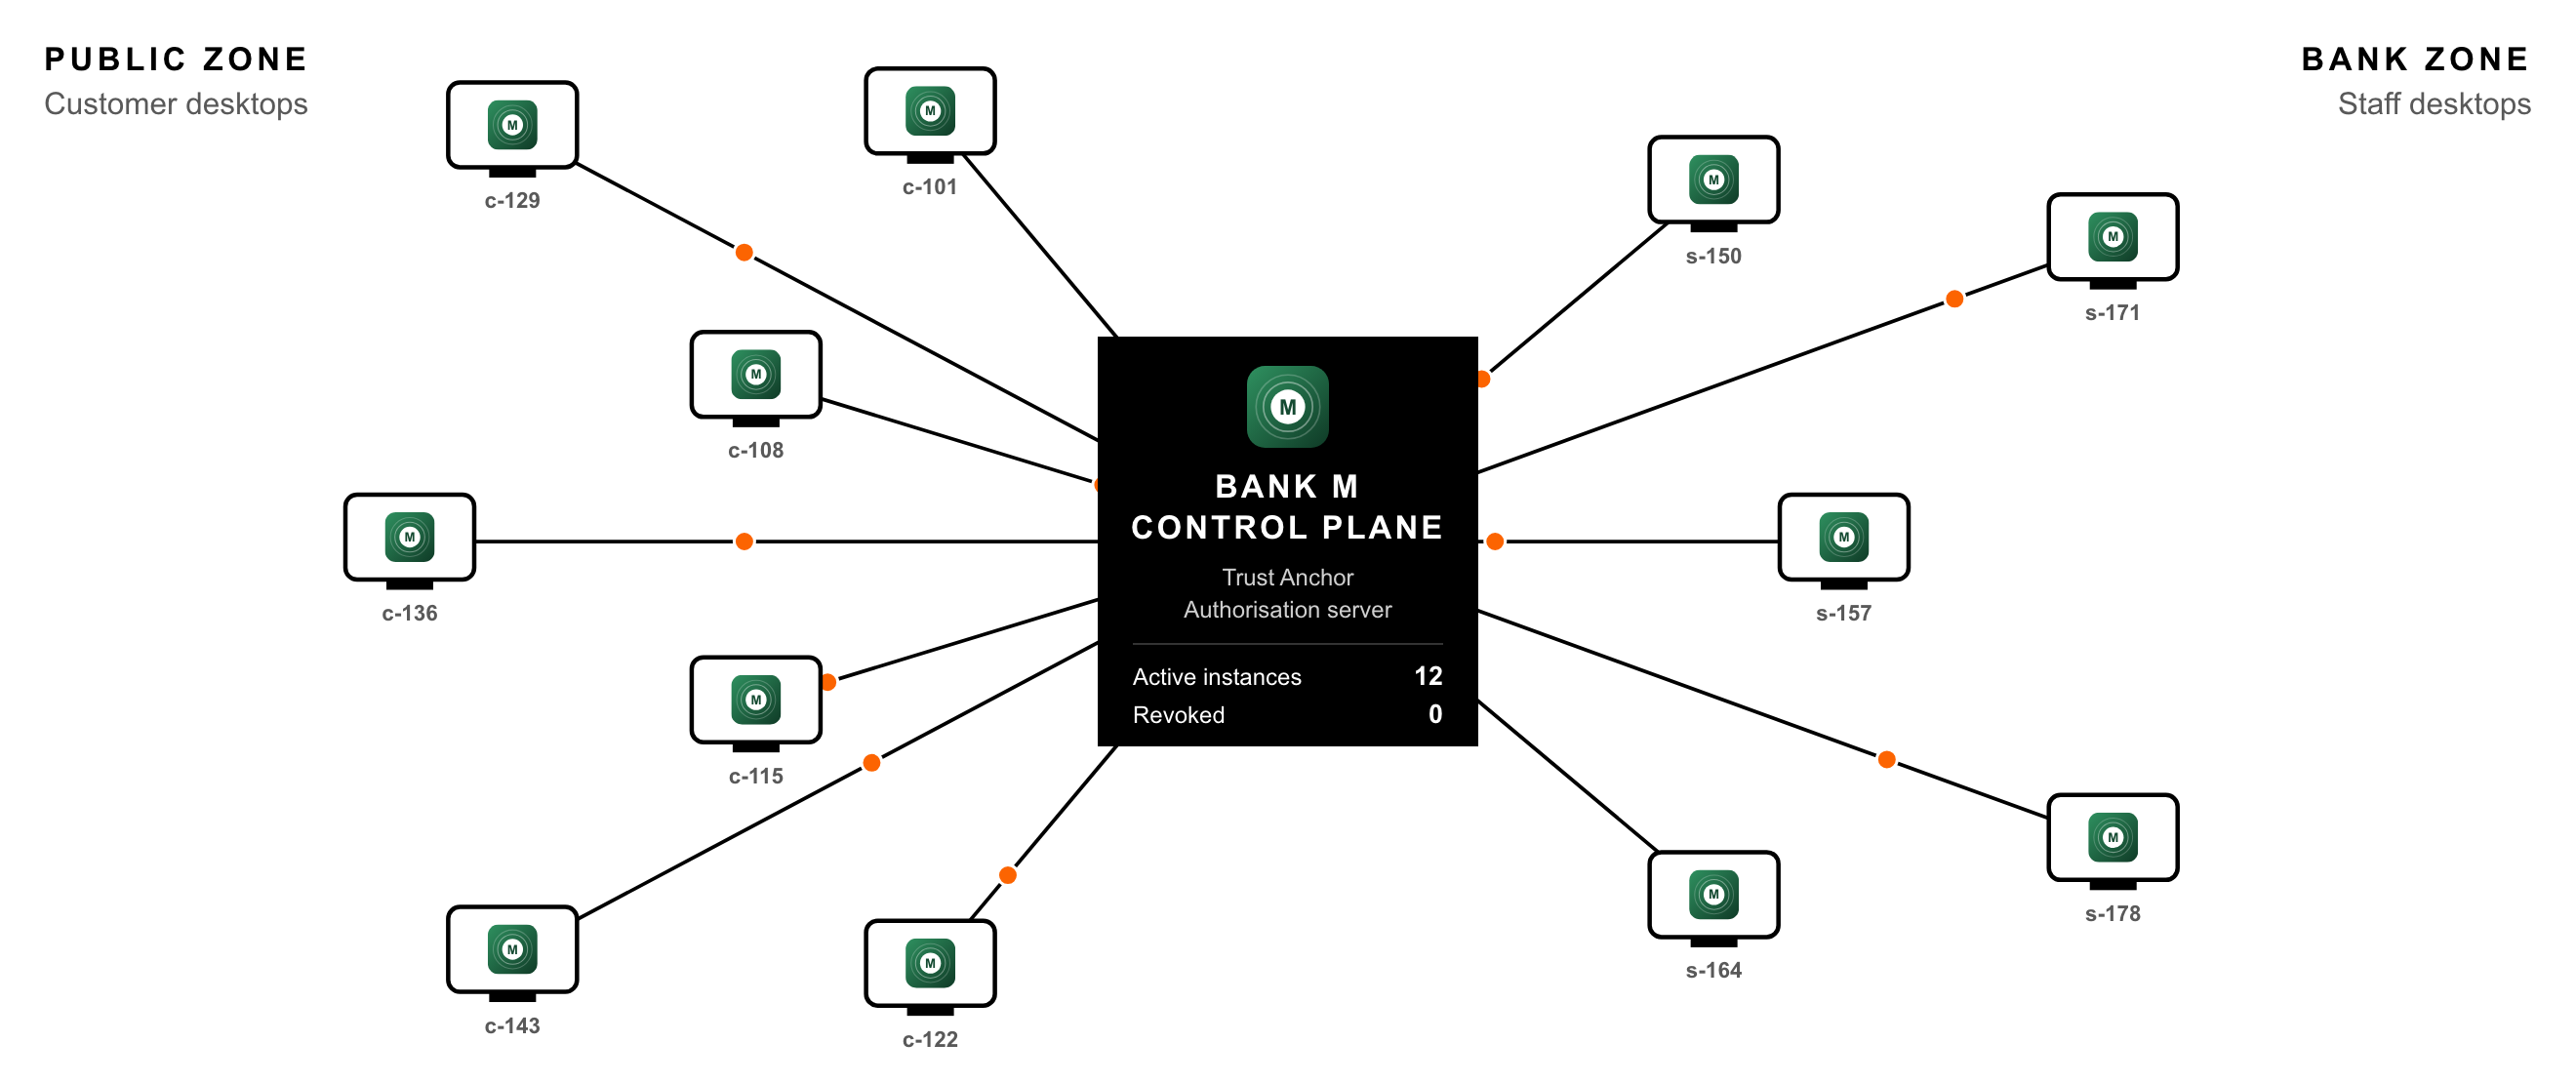
The bank lists every instance
Illustrative diagram.
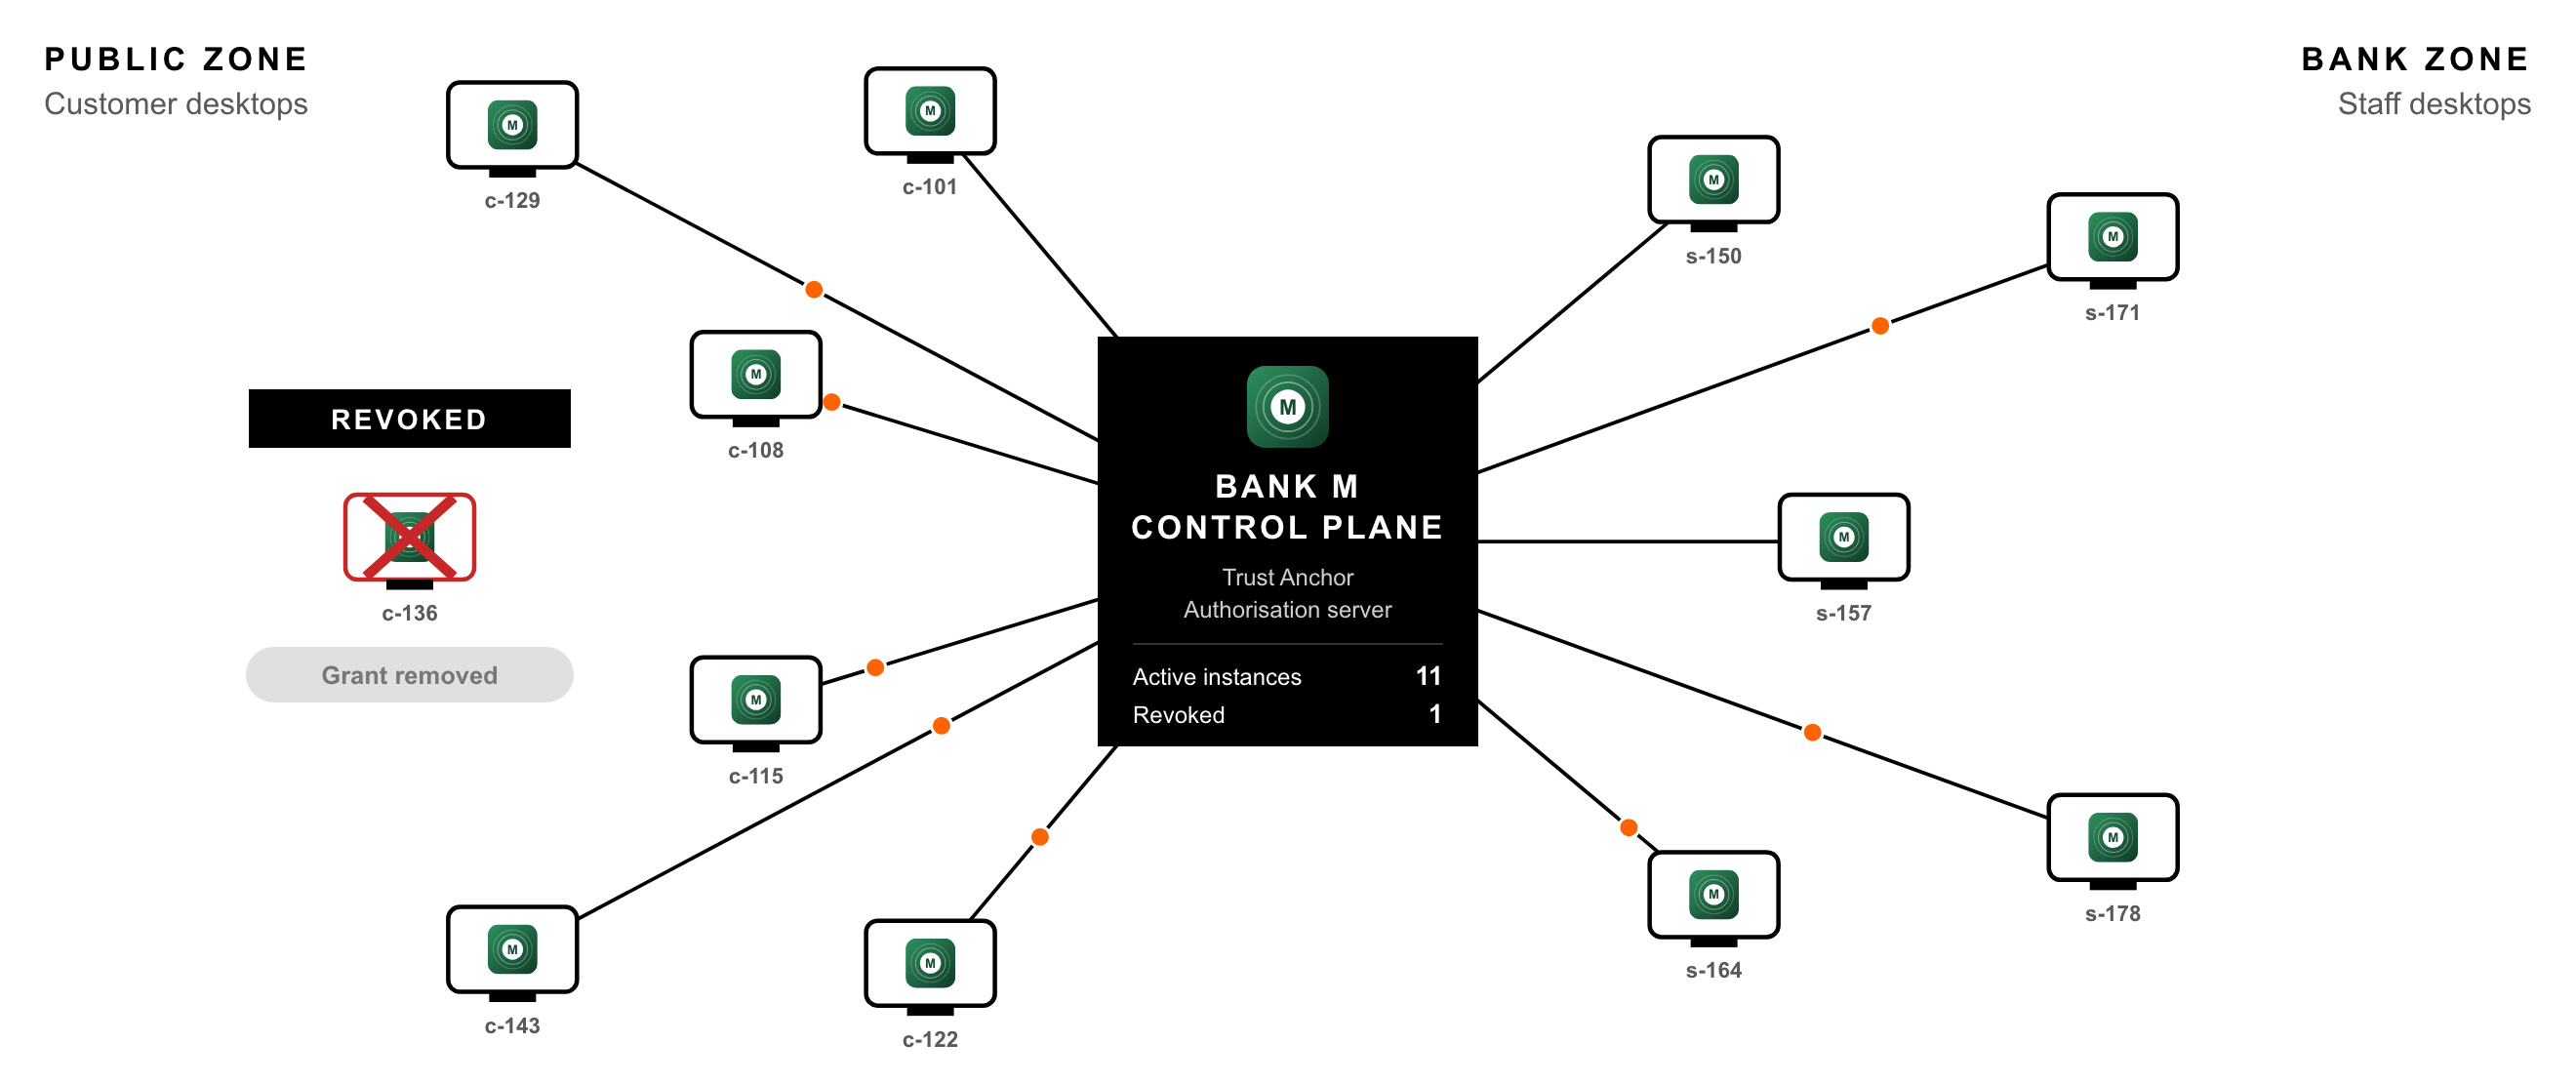
It revokes one at once
A risk on one desktop does not affect the others. Its grants are removed and every other instance keeps working.
Every control is a cryptographic check
The controls are enforced outside the AI, so they hold however capable the AI is.
The connector software is signed
The operating system checks the signature before the connector runs.
Each instance holds its own private key
The key stays on the device.
Each access token is bound to that key
A token copied to another machine does not work.
The bank's Trust Anchor signs the trust chain
The connector checks that it is talking to the real bank.
No prompt changes the result of a signature check.
The controls hold even when the AI does not behave.
What is built and what is proposed
Built and seen working
- A reference build in a bank demonstration environment, October 2026
- QR scan, Bluetooth check and six-digit code
- Accounts start as Not shared
- Access tokens bound to the instance's key
- The AI app asks before each tool use
Distributed today
- Desktop builds through TestFlight
- Customer connectors on macOS
- An app store listing is a concept for now
Proposed
- Revocation of any instance from the bank's control plane
- Connectors on staff desktops inside the bank
- A Windows version
- A path to post-quantum algorithms